We have received text from H.R. 10915: Common-Sense Cloud Security Act. This bill was received on 2026-10-26, and currently has no cosponsors.
Here is a short summary of the bill:
This bill would direct the National Institute of Standards and Technology (NIST) to develop new guidance on how to secure cloud computing systems.
What NIST would have to do
Within 180 days of enactment, NIST would have to ask for public comments on its current cloud cybersecurity standards and on possible new ones. The bill specifically calls for standards and recommendations on:
- Managing and securing digital identities used in cloud systems, including linking logins and access credentials to a device when appropriate.
- How cloud providers can monitor and respond to security alerts and suspicious or unauthorized activity.
- Preventing, detecting, and limiting attacks that happen within a cloud environment, including “east-west traffic” between systems inside the cloud.
- Reviewing, approving, and continuously monitoring third-party apps and software-as-a-service tools that connect to cloud environments.
- Using artificial intelligence tools to spot unusual or suspicious activity.
- Methods for determining the “blast radius,” meaning how far damage or unauthorized access could spread if part of a cloud system is compromised.
NIST would then have to publish a draft version of these standards within 50 days after the comment request, seek public comment on that draft, and publish a final version within 135 days after that.
Who NIST would consult
In developing the standards, NIST would be required to consult with several groups and agencies, including:
- The Department of Defense
- The National Cyber Director
- The Cybersecurity and Infrastructure Security Agency (CISA)
- Cloud service providers
- Owners and operators of critical infrastructure
- Industry groups in sectors such as banking, finance, and health care
- Academic or nonprofit organizations with expertise in cloud security and AI governance
Voluntary certification program
Within one year after the final standards are published, NIST and CISA would have to create a voluntary “Cloud Security Certification Program.” This program would:
- Use independent, accredited private testing labs to evaluate whether entities meet the standards.
- Cover topics like blast radius, intracloud attacks, third-party app integrations, and workload identity.
- Include a public database of certifications.
- Offer tiered certification levels.
- Require labs to make certification decisions within 90 days after an application is submitted.
Changes to federal cloud security rules
Within one year after the final standards are published, the Office of Management and Budget would have to update the Federal Risk and Authorization Management Program, or FedRAMP, so it matches the new NIST standards. As part of that update, private companies that provide cloud services to the federal government would have to disclose information about:
- Their overall potential blast radius
- How they monitor network traffic inside their cloud systems
- The scope and access levels of third-party app integrations in their cloud environments
Reporting to Congress
Within one year after the final standards are published, NIST would have to report to Congress on:
- How federal agencies are implementing the standards
- Any gaps or problems private companies face in adopting them
- Any recommended legislative or administrative changes related to cloud cybersecurity
Relevant Companies
- AMZN — Amazon Web Services could be affected by updated federal cloud security requirements and any certification framework tied to cloud providers serving the government.
- MSFT — Microsoft Azure could be affected by new standards for cloud security, federal procurement rules, and certification requirements.
- GOOGL — Google Cloud could be affected by the new cloud cybersecurity standards and possible certification or disclosure requirements for federal cloud vendors.
- ORCL — Oracle Cloud could be affected if federal cloud security rules and certification standards change for government-facing cloud services.
- CRM — Salesforce could be affected to the extent its cloud services and third-party integrations are subject to new cloud security standards or certification expectations.
- NET — Cloudflare could be affected by broader cloud security standards and requirements related to traffic inspection, monitoring, and security tooling.
- OKTA — Okta could be affected by standards focused on digital identity, login security, and credential management in cloud environments.
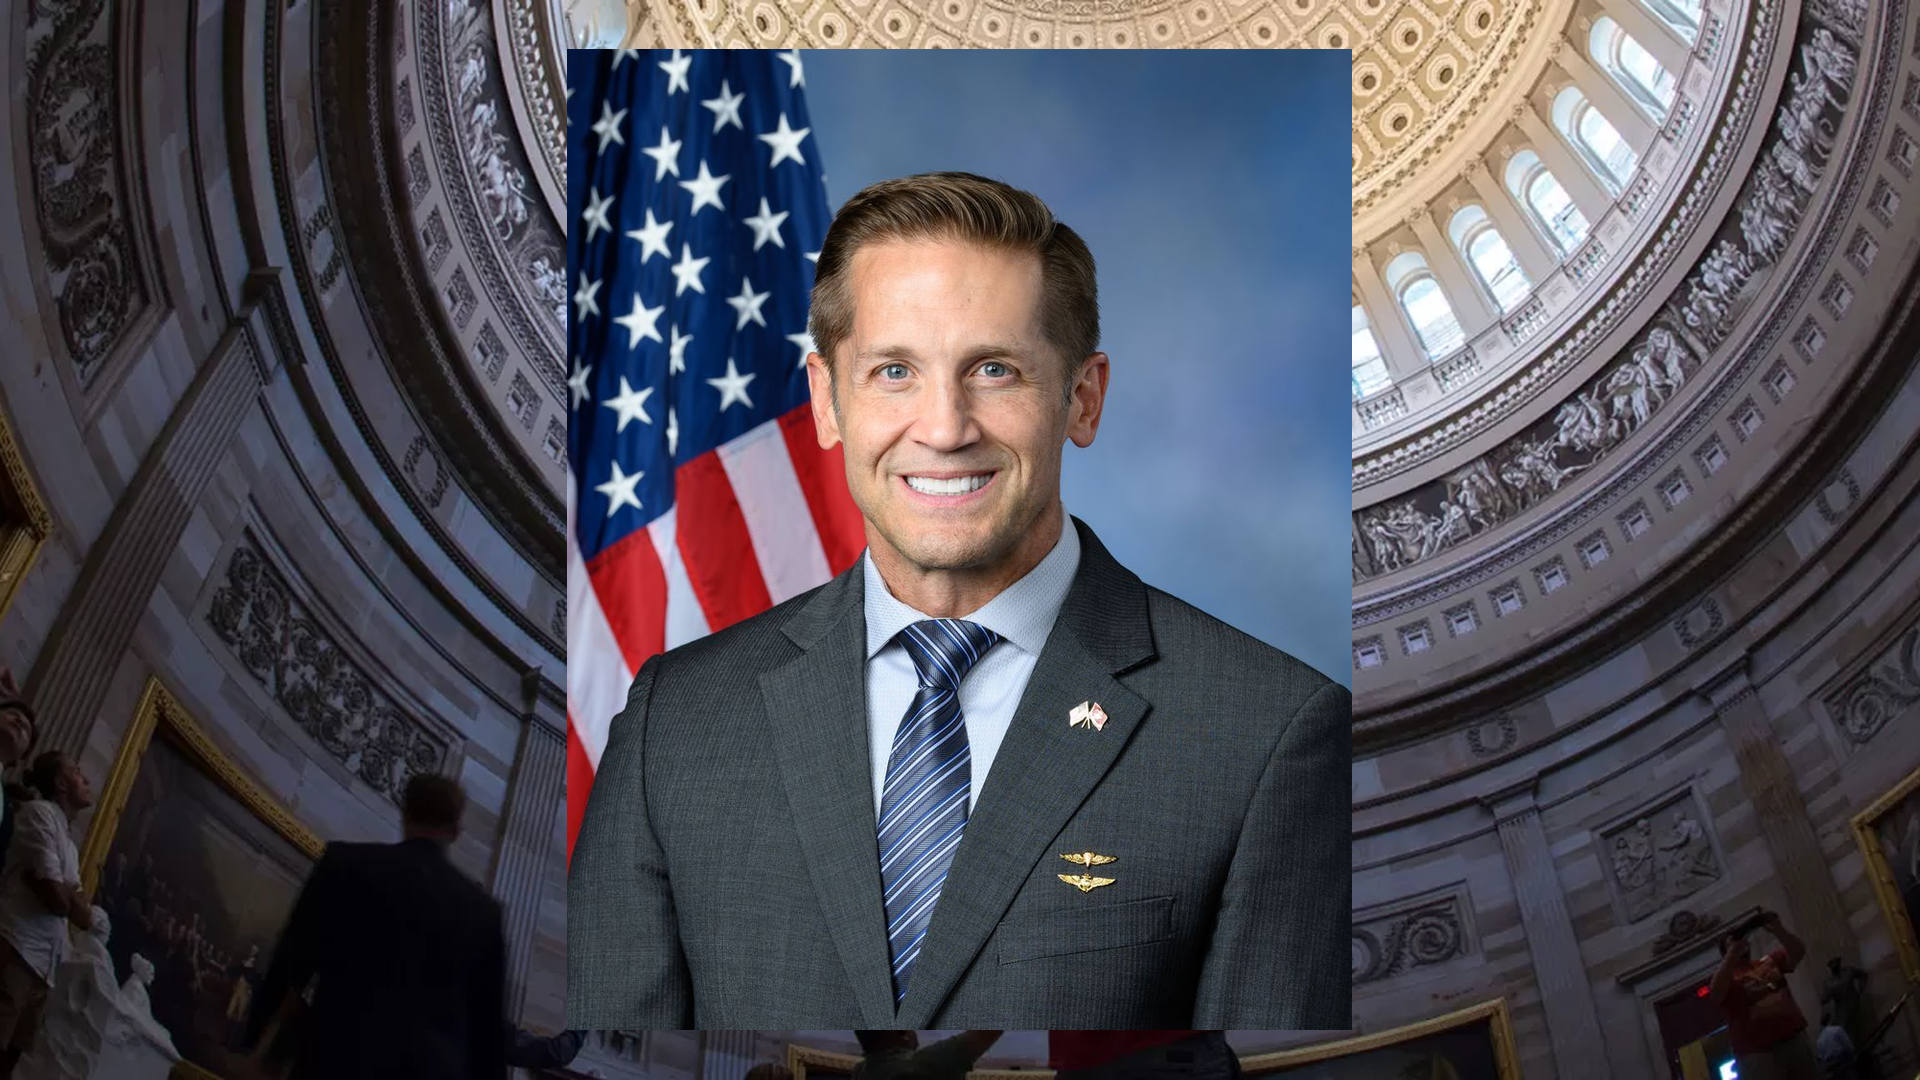
Representative Richard McCormick Bill Proposals
Here are some bills which have recently been proposed by Representative Richard McCormick:
- H.R.10915: To require the Director of the National Institute of Standards and Technology to develop new standards, methodologies, and recommendations with respect to the cybersecurity of cloud-based infrastructure, and for other purposes.
- H.R.10784: To amend the Internal Revenue Code of 1986 to provide home ownership assistance, and for other purposes.
- H.R.10501: Communist Control Act of 2026
- H.R.9991: STOP the SWAMP Act
- H.R.9919: Ban Birth Tourism Act of 2026
- H.R.9755: Biotechnology Diplomacy Leadership Act of 2026
You can track bills proposed by Representative Richard McCormick on Quiver Quantitative's politician page for McCormick.
Representative Richard McCormick Net Worth
Quiver Quantitative estimates that Representative Richard McCormick is worth $1.2M, as of October 28th, 2026. This is the 317th highest net worth in Congress, per our live estimates.
McCormick has approximately $315.0K invested in publicly traded assets which Quiver is able to track live.
You can track Representative Richard McCormick's net worth on Quiver Quantitative's politician page for McCormick.
Representative Richard McCormick Stock Trading
We have data on up to $2.1M of trades from Representative Richard McCormick, which we parsed from STOCK Act filings. Some of the largest trades include:
- A July 30th, 2026 sale of up to $15K of $LHX. The stock has fallen 4.6% since then.
- A March 15th, 2023 purchase of up to $15K of $EMR. The stock has risen 106.47% since then.
- A March 15th, 2023 purchase of up to $15K of $BLK. The stock has risen 79.83% since then.
- A July 30th, 2026 sale of up to $15K of $APD. The stock has risen 2.3% since then.
- A July 30th, 2026 sale of up to $15K of $ADI. The stock has risen 16.0% since then.
You can track Representative Richard McCormick's stock trading on Quiver Quantitative's politician page for McCormick.
2026 Georgia's 7th Congressional District Election
There has been approximately $3,802,230 of spending in Georgia's 7th congressional district elections over the last two years, per our estimates.
Approximately $207,639 of this has been from outside spending by PACs and Super PACs.
The rating for this race is currently "Solid R".
You can track this election on our matchup page for the 2026 Georgia's 7th congressional district election.
This article is not financial advice. See Quiver Quantitative's disclaimers for more information.